What you get
- Findings identified and prioritized by severity.
- PDF reports: a full technical report, an executive summary, or findings mapped to compliance standards.
- With the Web Agentic Deep Scan, findings validated with a proof-of-concept exploit.
Test the entry points of your web application across technologies and frameworks. Ostorlab crawls your application with session-aware navigation, then tests what it reaches, giving you a clear picture of your web app's security posture.
Integrate security testing for web applications seamlessly into your development processes with CI/CD, ticketing integrations, and SSO with 2FA. Streamline your workflows and ensure security is always a top priority.
Automate complex authentication with Puppeteer scripts recorded in Chrome's built-in Recorder, and complete two-factor steps (SMS, email or TOTP one-time codes) once your test account is set up. The same authenticated testing is available for mobile apps.
Open Web Application Security ProjectNational Institute of Standards and TechnologyInternet of Secure ThingsCompliance with standards such as the OWASP Top 10, PCI DSS, HIPAA or GDPR is crucial for building customer trust. Ostorlab helps you demonstrate compliance by identifying vulnerabilities and prioritizing them by severity, so you can show your applications meet the required security standards.
Ostorlab combines detection techniques such as Chrome-based XSS testing with polyglot payloads, probabilistic backend injection testing that avoids sending full payloads, and checks for actively exploited vulnerabilities from the CISA KEV catalog.
Gain visibility into intercepted traffic, discovered endpoints and crawl coverage. With Ostorlab, you can see what attackers see and save hours of tool runs and output grouping.
Guidance for your team
Ostorlab turns a scan into a prioritized plan: what to fix first, why it matters and how to fix it, using the context you add about your app.
Scan > AI recommendationsAdd contextBefore you start
No mobile app needed. Scan web apps and APIs on their own, from a URL, a domain or an API schema.
 Autonomous Pentesting vs. Traditional Penetration Testing: Where Agentic AI Delivers—and Where Humans Still LeadRead
 New Dashboard UI, On-Premises Scanner, Agentic Scan Knowledge, Multi-Asset Scanning, Linear & MCP Integrations, and New Model SupportRead
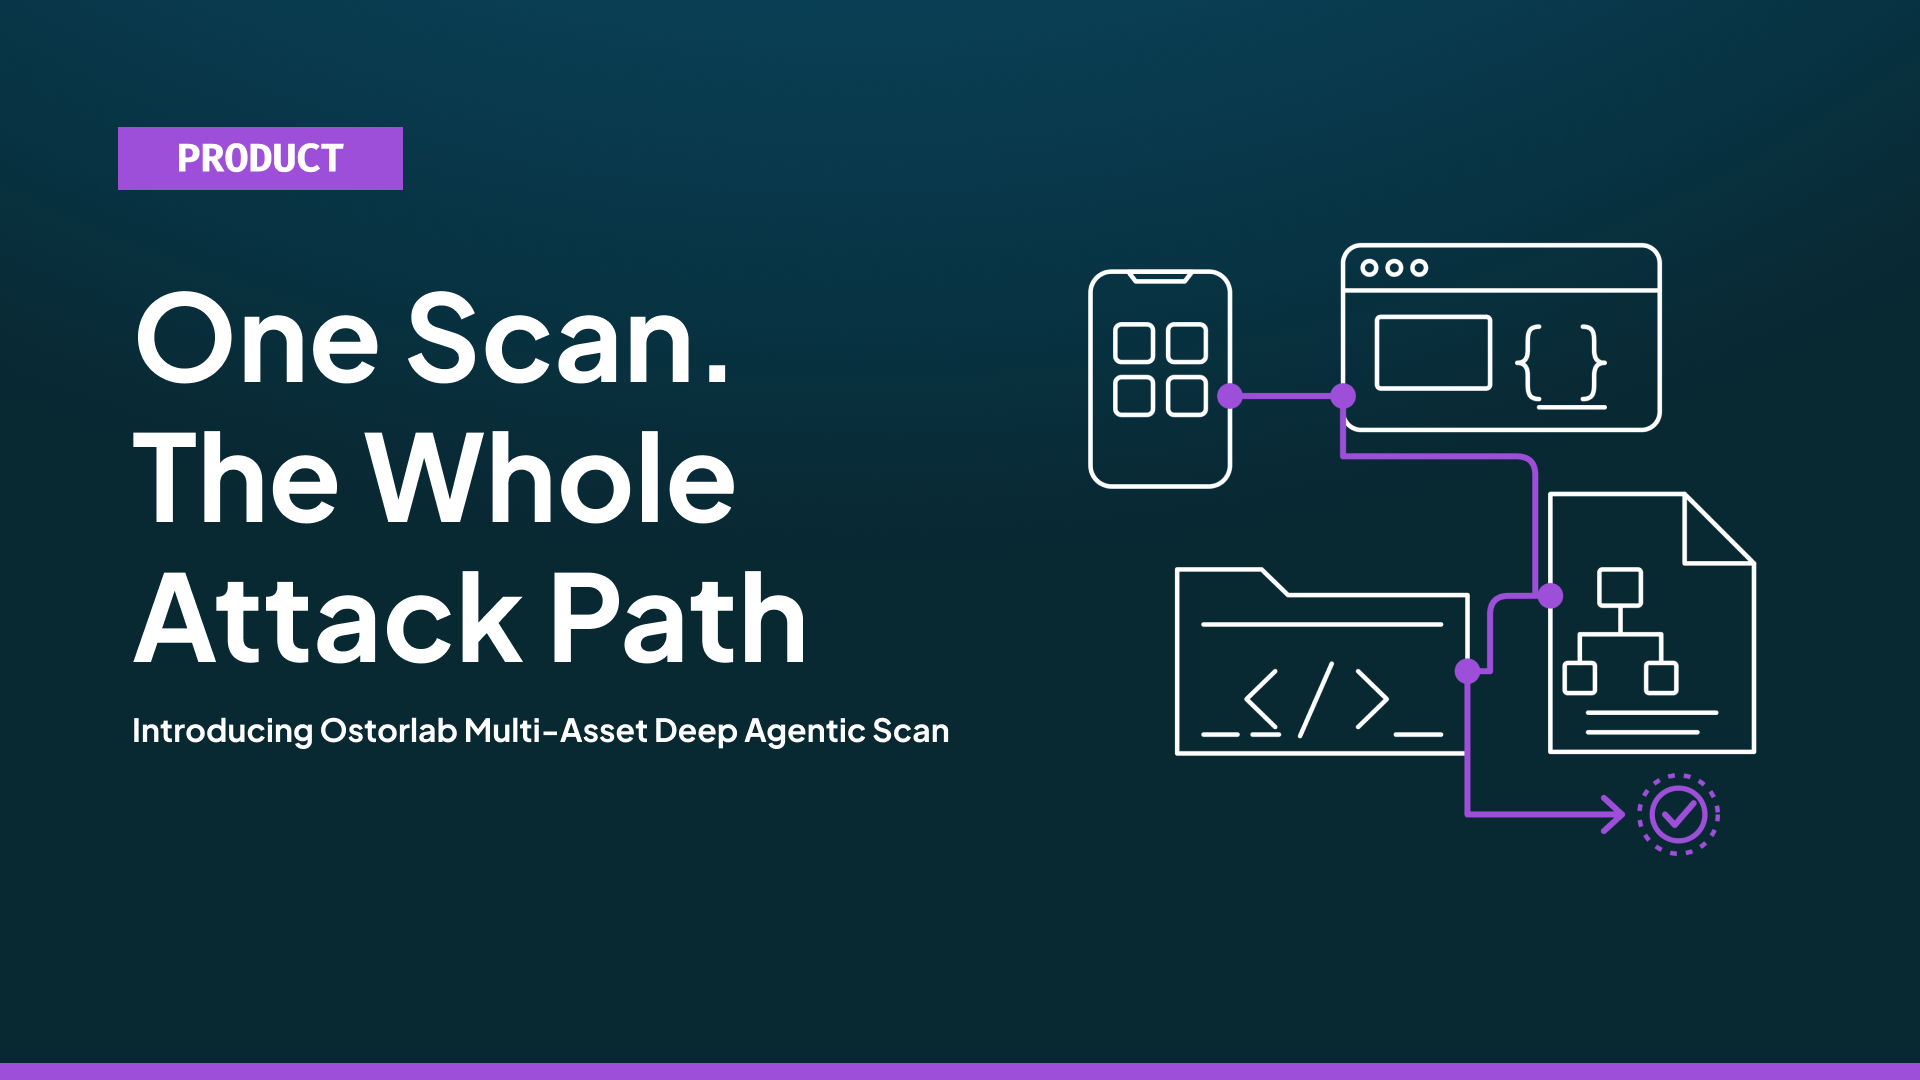 Introducing Multi-Asset Deep Agentic Scan: Connected Testing Across the ApplicationRead
 Bypassing Mobile App Shielding: Where Detection Ends and Enforcement FailsRead
Very efficient team, the support engineers are very good and knowledgeable. The product is always evolving and they take customer input very seriously.
Gartner® and Peer Insights™ are trademarks of Gartner, Inc. and/or its affiliates. All rights reserved. Gartner Peer Insights content consists of the opinions of individual end users based on their own experiences, and should not be construed as statements of fact, nor do they represent the views of Gartner or its affiliates. Gartner does not endorse any vendor, product or service depicted in this content nor makes any warranties, expressed or implied, with respect to this content, about its accuracy or completeness, including any warranties of merchantability or fitness for a particular purpose
Trusted worldwide
Security teams use Ostorlab's AI agents to test every release of their mobile apps, and developers get findings with a working exploit and a fix they can act on.