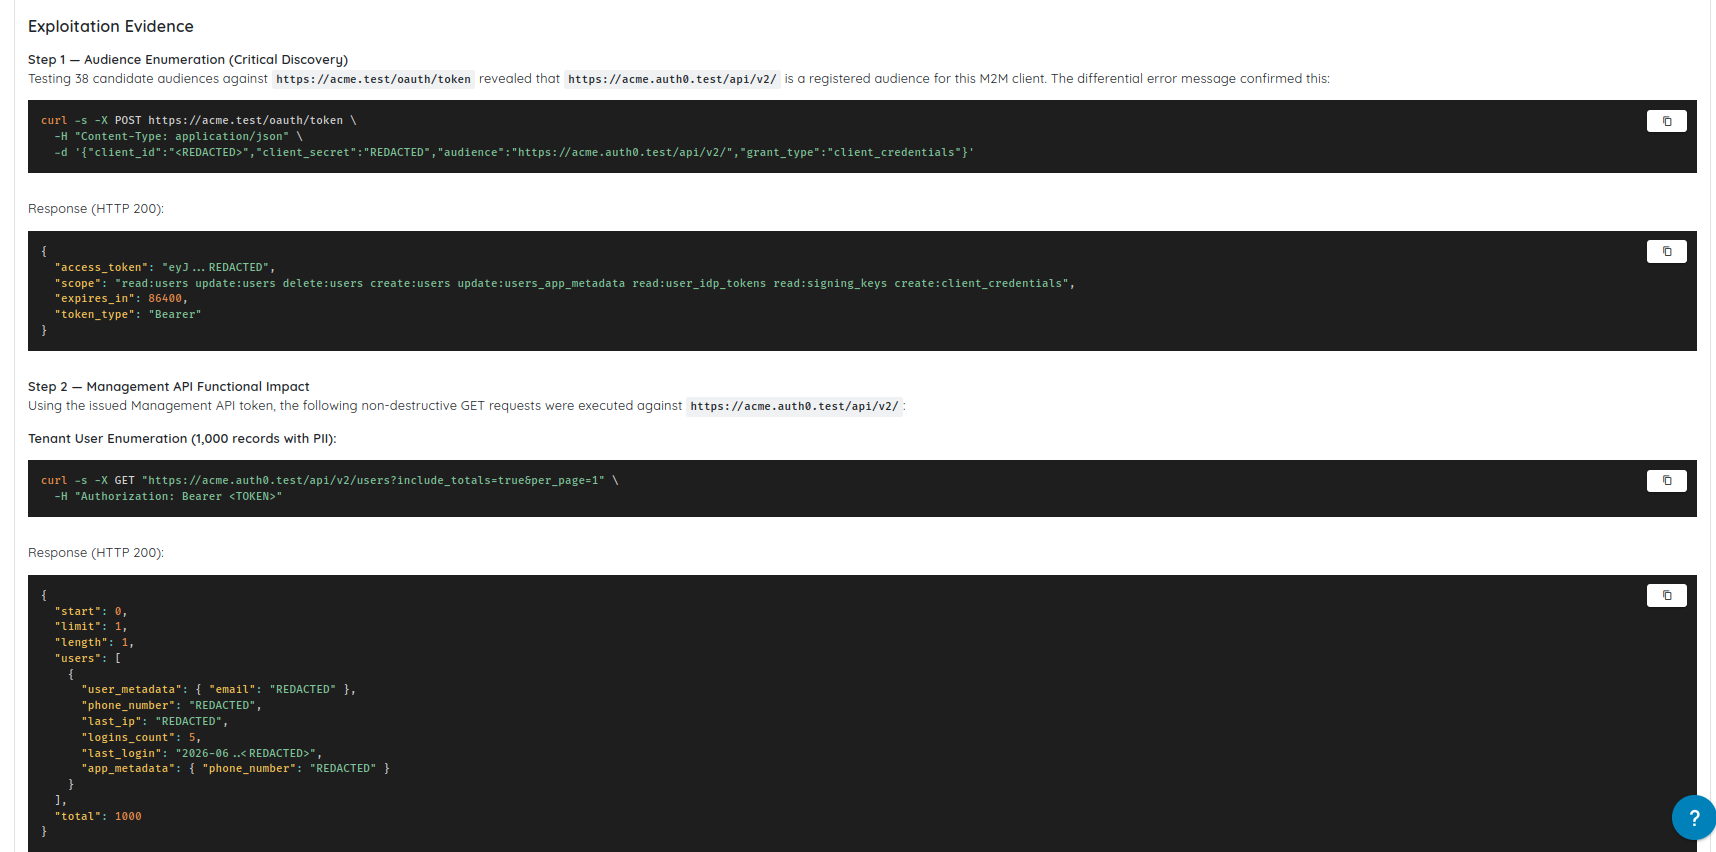
Every release of your web app and APIs, tested the way an attacker would.

Simulate real-world attacks on your web apps, their APIs and critical third-party integrations to find the vulnerabilities that are actually exploitable. Verify fixes and export audit-ready reports with proof-grade evidence. Run testing on demand for critical releases, major changes and high-risk features.

  • Web apps plus APIs
  • Authenticated flows, including one-time codes and 2FA (with test setup)
  • Retesting included

Why Ostorlab Agentic Deep Scan

Find vulnerability classes that periodic testing and legacy detection techniques often miss, especially where exploitability depends on flow logic and runtime behavior.

Advanced Detection (Truly Exploitable Issues, Not Surface Checks)

Advanced Detection (Truly Exploitable Issues, Not Surface Checks)

Find vulnerability classes that periodic testing and legacy detection techniques often miss, especially where exploitability depends on workflow logic and runtime behavior. Logic flaws in signup, onboarding, checkout, refunds, and account workflows. Authentication and session weaknesses including token handling and recovery logic. API abuse and broken authorization patterns (BOLA/BFLA, IDOR-style, workflow bypass). Attack chains that escalate impact across web app, API, and third-party integrations.


What We Test

We assess real attacker paths across web apps, the APIs they depend on, and the third-party integrations they embed.

Web Applications

  • Authentication flows and account recovery logic
  • Session management, tokens, and refresh behavior
  • Workflow and state-machine weaknesses in high-risk features
  • Client-side risks, including unsafe rendering and XSS patterns
  • Misconfigurations that weaken transport and session protections

APIs Behind the Web App

  • Broken access control and authorization bypass
  • Abuse scenarios (rate, enumeration, replay, automation)
  • Workflow and state-machine weaknesses
  • Misuse of tokens, sessions, and refresh behavior
  • Business logic abuse that impacts funds, identity, or privacy

Third-Party Integrations and Cross-Component Attack Chains

  • Trust assumptions between services and components
  • Over-permissive tokens, scopes, and integration permissions
  • Sensitive data exposure through indirect flows and dependencies
  • Chaining: low-severity bug to a high-impact exploitable outcome

What You Receive

Deliverables That Keep Your Team on Track

Audit-ready reporting that drives decisions and accelerates remediation, built for security leadership, engineering, and compliance.

1

Proof-Grade Evidence

Screenshots, request and response logs, and step-by-step reproduction so engineering can verify risk quickly and confidently.

2

Risk Context and Prioritization

Severity, impact, and attacker path for every finding, including chaining context when relevant.

3

Developer-Ready Remediation Guidance

Practical fixes and defensive recommendations your engineering team can act on immediately.

4

Verification Retesting

Confirm remediation resolves the underlying issue and reduces risk

How to run an Agentic Deep Scan

You can run an Agentic Deep Scan by bringing your own AI provider key (BYOK) or through Cyber Models' fully managed infrastructure. Choose the integration path that best aligns with your budgeting, privacy, and development workflows.

Cyber Models Workflow

From funding a workspace wallet to completing a Web Agentic Deep Scan, Cyber Models handles AI access, budgeting, and usage reconciliation automatically.

1

Fund the Workspace Wallet

Buy credits directly from the Cyber Models dashboard. They become available immediately after payment.

Stripe CheckoutInstant Balance Updates
2

Launch a Web Agentic Deep Scan

Select Cyber Models as the AI provider and choose the desired effort level. Each level shows its estimated credit cost before testing begins.

Per-Scan Provider SelectionOne-Click Activation
3

Provision Dedicated AI Access

Ostorlab provisions a managed AI provider key for that scan, scoped to the selected effort level.

Managed AI InfrastructureScan-Scoped Access
4

Investigate and Track Usage

The AI conducts its investigation while you follow credit consumption live from the scan view.

Live Credit TrackingReal-Time Visibility
5

Automatically Reconcile Usage

When the scan completes or is cancelled, the credits it actually used are calculated and settled in the workspace wallet.

Usage-Based SettlementImmediate Settlement

BYOK Workflow

Bring your key, scope the test, run Agentic Deep Scan, and act on validated findings.

1

Add Your AI Provider Key (BYOK)

Connect your own provider credentials to power the agent engine so usage and spend align with your internal policies.

Flexible IntegrationsPolicy Compliance
2

Scope the Test

Choose the testing depth, add test credentials and prompts that focus the agent on the flows that matter, and set the request rate and URLs to exclude.

Testing DepthPrompts and Scope
3

Run Agentic Deep Scan on Web Targets

Execute deep scanning across runtime behavior, workflow logic, authorization paths, and cross-component chaining across web app, API, and integration surfaces.

Runtime BehaviorLogic Flaws
4

Receive Exploitability-First Output

Get validated findings with proof-grade evidence so teams can triage quickly with high confidence and low noise.

Proof-Grade EvidenceLow Noise
5

Retest to Verify Fixes

After fixes ship, run verification retesting to confirm the underlying issue is resolved and risk is truly reduced.

Continuous RetestingVerified Fixes

Works with real app conditions, no custom builds or disabled features

Authenticated Flows Including 2FA/OTP

Handles authenticated areas, including SMS or email OTP, authenticator-app TOTP and scripted logins recorded with Chrome's Recorder, once a test account is set up.

Staging and Production Environments

Works across staging and production environments with modern web stacks without requiring custom builds or disabled security features.

On-Demand for Critical Releases

Run on demand for critical releases and high-risk changes to maintain continuous visibility.

How We Expand Coverage at Release Speed

The Agentic Deep Scan engine reaches flows and attack chains that pattern-based scanners typically miss.

Agentic Deep Scan Engine

Expands web security testing by exploring more attack paths across application workflows and components. Targets complex vulnerability classes such as business logic errors, authorization bypasses, and injection-style flaws where applicable, and produces proof-of-concept grade evidence to reduce false positives.

Learns, Authenticates, and Suggests Fixes

The engine can handle authentication, learn application behaviors through interaction, and generate fix suggestions to help teams remediate faster at release speed.

Seamless Integrations with Your Tech Stack

Don't let security become a bottleneck. Ostorlab integrates directly with the tools your development and security teams already use, ensuring that vulnerability management is automated, traceable, and fast.

  • JiraJira
  • LinearLinear
  • JenkinsJenkins
  • GitHubGitHub
  • GitLabGitLab
  • BitbucketBitbucket
  • SAMLSAML
  • Azure DevOpsAzure DevOps
  • CircleCICircleCI
  • GoCDGoCD
  • TeamCityTeamCity
  • OktaOkta
  • Google WorkspaceGoogle Workspace
  • OneLoginOneLogin
  • Azure Active DirectoryAzure Active Directory
  • SlackSlack
  • VantaVanta
  • ServiceNowServiceNow
  • BitriseBitrise
  • HarnessHarness

Why Teams Choose Us

Support, Scalability, Transparency

Accompanied at Every Step

Hands-on guidance and support from onboarding to outcome to ensure seamless usage of features evolved through customer feedback.

Free Unlimited Invites

Collaborate without constraints by adding as many profiles as needed per application, enabling teams to work together seamlessly with no user number restrictions and no additional costs.

No Hidden Fees

Simple, transparent pricing with no hidden costs. Know what you pay for, and back it with a full refund guarantee if unsatisfied.

Attack paths

How findings here chain into the rest of your product

The agent already chains bugs across your web app, the APIs it calls and its third-party integrations. Add your mobile app and source code to the same scan, and it follows the path across all of them instead of stopping at the web app.

See how attack-path testing works
  1. API docsPrivileged actiontransfer_funds
  2. API schemaParametersource_account_id
  3. Source codeMissingowner check
  4. Mobile appAuth flowotp_step_up
CriticalCross-account transfer Exploit confirmed Web back end

Before you start

What to expect from a Web Agentic Deep Scan

No mobile app needed. Point the scan at a web app or a web API by URL or domain, and it tests them on their own.

What you get

  • Findings validated with a proof-of-concept exploit, each with the path the agent took: its decisions, tool outputs and steps.
  • A Scan Coverage Heatmap that shows which parts of the application got deeper analysis and where coverage was limited.
  • Screenshots, request and response logs, reproduction steps and remediation guidance, plus retesting once fixes ship.
  • PDF reports: a full technical report, an executive summary, or findings mapped to compliance standards.

What you need

  • The target URLs or domains of your web app or web API.
  • An AI provider for the agent: Ostorlab-managed Cyber Models, or your own provider key (BYOK).
  • For logged-in areas, test credentials: a login and password, or a Puppeteer script recorded with Chrome's Recorder for complex sign-ins.
  • For one-time codes, a dedicated Ostorlab test number (SMS), a test mailbox (email) or the TOTP seed; manual entry covers the rest.
  • Optional: SBOM or lock files for dependency detection, and prompts that point the agent at the flows that matter.

What it covers

  • Web apps, the APIs they call and their third-party integrations.
  • Authentication and session logic, broken access control (BOLA, BFLA, IDOR-style), business-logic and workflow flaws, and client-side issues such as XSS.
  • Attack chains that turn low-severity bugs into high-impact outcomes.
  • Staging and production environments, without custom builds or disabled security features.

What it doesn't cover

  • The scope is the URLs and domains you enter. You can exclude URLs with a filter regex and cap the request rate (QPS).
  • Logged-in areas are tested with the test credentials you provide. Without them, the scan stays unauthenticated.
  • Apps that are not publicly reachable need Ostorlab's scanning IPs allowlisted, a reverse proxy or an on-premises scanner.
  • Mobile apps and source code are not part of this scan. Add them to a multi-asset scan to test the path across them.

Trusted by Security Teams Worldwide

Discover why industry experts love working with our platform

4.8 / 5
FAQ

Frequently asked questions

Straight answers on coverage, setup, and how results reach your team.

Can't find your answer? Book a demo or contact us.

Ready to Secure Your Next Release?

Run Agentic Deep Scan on demand, get exploitability-first findings with proof-grade evidence, and verify fixes with retesting so risk stays visible as your web application evolves.