






From Signal to the Android SDK: Chaining Path Traversal, Mimetype Confusion, Security Check Bypass and File Descriptor Bruteforce for Arbitrary File AccessRead more →
Investigate Mobile Vulnerabilities Beyond Detection
Turn a flagged mobile vulnerability into actionable risk insight with an AI-powered follow-up investigation. Dig Deeper helps security teams validate findings, uncover technical context, explore potential exploitation paths, and prioritize remediation with greater confidence.
- Verify False Positives
- Run Deeper Investigations
- Perform Custom Actions
Trusted by security teams at
Go beyond the initial finding
A vulnerability finding is only the starting point. Security teams still need to determine whether an issue is real, how it can be exploited, and what action to take next. Dig Deeper adds a focused investigation layer directly inside Ostorlab, helping teams move from detection to validation, context, and decision-making.
1
Validate findings with focused follow-up assessments
Launch a targeted investigation from any vulnerability result to confirm whether the issue is valid, reduce false positives, and understand the real impact before escalating or remediating.
2
Investigate exploitability with more context
Go deeper into a finding to uncover supporting evidence, technical details, and potential exploitation paths. Dig Deeper helps teams better assess severity, understand attack scenarios, and focus on what matters most.
3
Guide investigations with specialized actions
Choose from built-in investigation paths or provide custom instructions for specialized analysis. This gives teams the flexibility to adapt the workflow to the finding, the environment, and the question they need answered.
Dig Deeper Features
Verify Mobile False Positives
Cut through noise faster by running a focused follow-up assessment on a single finding. Dig Deeper helps teams quickly confirm whether an issue is real, reduce alert fatigue, and triage with more confidence.
Expose the Real Risk
Go beyond the initial alert to uncover deeper context, identify supporting signals, and explore possible exploitation paths. This helps teams better understand impact and focus on the vulnerabilities that truly matter.
Tailor Each Investigation
Not every finding fits a standard workflow. With custom actions, teams can provide their own prompts and guide the investigation toward specialized validation steps, targeted technical checks, or deeper analysis.
Put AI to Work on Any Finding
Dig Deeper uses AI-powered investigation workflows to help teams validate findings, enrich context, and move from raw detection to actionable risk insight faster.
Get Started Without the Complexity
A simple AI provider setup lets one model power the entire workflow, so teams can start using Dig Deeper quickly without added operational overhead.
Use the Right Model for the Right Task
Advanced multi-model configuration gives teams more control over how investigations run by assigning specialized models to different stages of the workflow, balancing accuracy, speed, and cost.
Turn Findings Into Actionable Risk Insight
Dig Deeper helps security teams answer the questions that matter after a scan:
Is this vulnerability real?
Does it deserve prioritization?
What evidence supports the finding?
Are there plausible exploitation paths?
What additional investigation should happen next?
Single Vulnerability Assessment (SVA)
Targeted Testing on Demand
Run a targeted test against one specific vulnerability or security objective and get a clear answer in minutes, without re-running a full scan.
Key Capabilities and Use Cases
Faster Fix Verification
Validate that a newly deployed patch or configuration change has closed a specific vulnerability. SVA lets your team re-test on demand, confirming the fix holds before a ticket is closed.
Streamlined Bug Bounty Triage
Feed a researcher submission into SVA to replicate and validate the individual finding, turning raw external reports into structured, actionable engineering data.
Cost-Effective Security Spot Checks
Run focused, single-objective security checks whenever a specific risk or compliance requirement arises. SVA concentrates on the target issue, delivering fast results without the noise of a full scan.
Simple by default, flexible when needed
Dig Deeper and SVA support two modes of AI provider configuration.
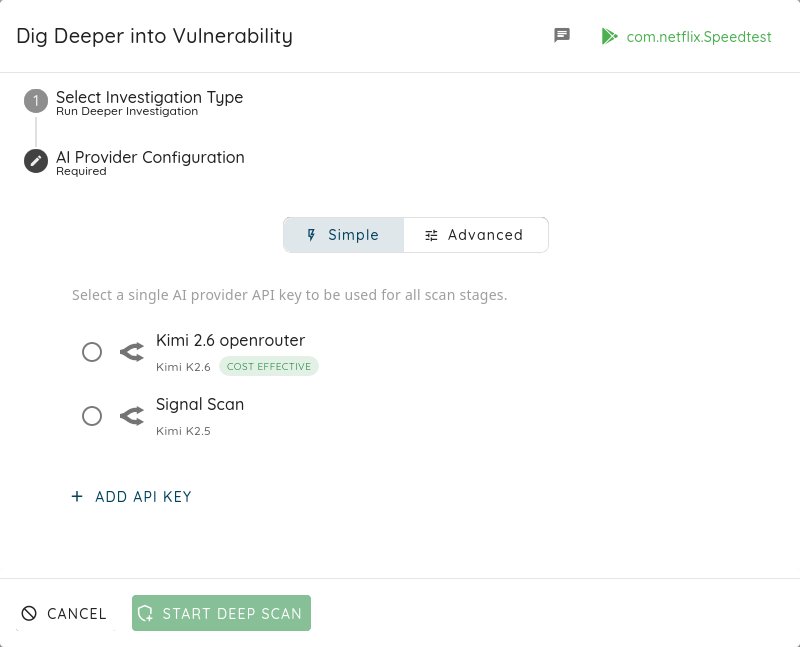
Simple Mode
Use one AI model for the full investigation workflow. Ideal for teams that want the easiest setup and a fast path to value.
Seamless Integrations with Your Tech Stack
Don't let security become a bottleneck. Ostorlab integrates directly with the tools your development and security teams already use, ensuring that vulnerability management is automated, traceable, and fast.
 Jira
 Linear
 Jenkins
 GitHub
 GitLab
 Bitbucket
 SAML
 Azure DevOps
 Microsoft AppCenter
 CircleCI
 GoCD
 TeamCity
 Okta
 Google Workspace
 OneLogin
 Azure Active Directory
 Slack
 Vanta
 ServiceNow
 Bitrise
 Harness
Trusted by Security Teams Worldwide
Discover why industry experts love working with our platform


Very efficient team, the support engineers are very good and knowledgeable. The product is always evolving and they take customer input very seriously.
A reliable product with unique features and a personalized approach to products.
The platform helped us evaluate our internal mobile applications easily and efficiently. The onboarding was smooth and the UI dynamic automation is great.
The product meets our needs perfectly and is easy to set up and use. The team is very reactive.
Very professional and technical. Five star. Excellent delivery.
We selected Ostorlab as our sole partner in providing mobile applications and web vulnerability scans. We have a very good partnership.
Their customer service is top notch and their product is constantly improving.
Easy to use and getting better with new updates, they are also quick to help and very efficient.
Great product, with amazing customer service, very useful, accurate, and straightforward to use.
Prompt support and personalized features highlighted.
I had a very excellent experience with Ostorlab as a MAST solution.
Very efficient team, the support engineers are very good and knowledgeable. The product is always evolving and they take customer input very seriously.
A reliable product with unique features and a personalized approach to products.
The platform helped us evaluate our internal mobile applications easily and efficiently. The onboarding was smooth and the UI dynamic automation is great.
The product meets our needs perfectly and is easy to set up and use. The team is very reactive.
Very professional and technical. Five star. Excellent delivery.
We selected Ostorlab as our sole partner in providing mobile applications and web vulnerability scans. We have a very good partnership.
Their customer service is top notch and their product is constantly improving.
Easy to use and getting better with new updates, they are also quick to help and very efficient.
Great product, with amazing customer service, very useful, accurate, and straightforward to use.
Prompt support and personalized features highlighted.
I had a very excellent experience with Ostorlab as a MAST solution.
Very efficient team, the support engineers are very good and knowledgeable. The product is always evolving and they take customer input very seriously.
A reliable product with unique features and a personalized approach to products.
The platform helped us evaluate our internal mobile applications easily and efficiently. The onboarding was smooth and the UI dynamic automation is great.
The product meets our needs perfectly and is easy to set up and use. The team is very reactive.
Very professional and technical. Five star. Excellent delivery.
We selected Ostorlab as our sole partner in providing mobile applications and web vulnerability scans. We have a very good partnership.
Their customer service is top notch and their product is constantly improving.
Easy to use and getting better with new updates, they are also quick to help and very efficient.
Great product, with amazing customer service, very useful, accurate, and straightforward to use.
Prompt support and personalized features highlighted.
I had a very excellent experience with Ostorlab as a MAST solution.
FAQ
Frequently asked questions
Straight answers on coverage, setup, and how results reach your team.
Can't find your answer? Book a demo or contact us.
Get Started with Dig Deeper
Validate findings, investigate vulnerabilities with more depth, and turn detection into actionable risk insight.