






Introducing Ostorlab’s Single Vulnerability Assessment and Dig DeeperRead more →
Investigate Web Vulnerabilities Beyond Detection
Investigate a specific web finding, test a custom attack hypothesis, or validate a fix without repeating a full assessment. Dig Deeper adds technical context and targeted testing to your existing results; confirmed AI-agent findings already include exploit evidence.
- Investigate Potential Findings
- Run Deeper Investigations
- Test Custom Hypotheses and Fixes
Trusted by security teams at
Go beyond the initial finding
Confirmed AI-agent findings already come with exploit evidence. Use Dig Deeper when you want to investigate a potential finding from another scan engine, explore a further attack path, test a custom hypothesis, or check a fix.
1
Investigate potential findings
Run a focused investigation on a potential finding to assess whether it is exploitable and capture evidence of its impact. Potential findings remain distinct from confirmed AI-agent findings.
2
Investigate exploitability with more context
Explore additional impact, related attack paths or a different scenario around a finding. Guide the agent toward the technical question your team needs answered.
3
Guide investigations with specialized actions
Choose a built-in action or provide custom instructions to test an attack hypothesis, investigate a specific behavior, or validate a deployed fix.
Dig Deeper Features
Triage Potential Findings
Investigate a potential finding from a scan engine with targeted checks and reproduction evidence, so your team can decide whether to escalate it.
Expose the Real Risk
Go beyond the initial alert to uncover deeper context, identify supporting signals, and explore possible exploitation paths. This helps teams better understand impact and focus on the vulnerabilities that truly matter.
Tailor Each Investigation
Not every finding fits a standard workflow. With custom actions, teams can provide their own prompts and guide the investigation toward specialized validation steps, targeted technical checks, or deeper analysis.
Put AI to Work on Any Finding
Use AI agents for a focused follow-up: investigate a potential finding, explore a custom attack scenario, or validate remediation. Confirmed AI-agent findings already carry exploit evidence from the original assessment.
Get Started Without the Complexity
Use Ostorlab-managed Cyber Models with credits, or connect your own AI provider key. Choose the setup that fits your team’s workflow.
Use the Right Model for the Right Task
Advanced multi-model configuration gives teams more control over how investigations run by assigning specialized models to different stages of the workflow, balancing accuracy, speed, and cost.
Turn Findings Into Actionable Risk Insight
Choose the question for a targeted investigation:
Can this potential finding be reproduced?
Does it deserve prioritization?
What additional impact can this finding have?
Does our custom attack hypothesis work?
Has the deployed fix closed the vulnerability?
Single Vulnerability Assessment (SVA)
Targeted Testing on Demand
Run a targeted test against one specific vulnerability or security objective and get a clear answer in minutes, without re-running a full scan.
Key Capabilities and Use Cases
Faster Fix Verification
Validate that a newly deployed patch or configuration change has closed a specific vulnerability. SVA lets your team re-test on demand, confirming the fix holds before a ticket is closed.
Streamlined Bug Bounty Triage
Feed a researcher submission into SVA to replicate and validate the individual finding, turning raw external reports into structured, actionable engineering data.
Cost-Effective Security Spot Checks
Run focused, single-objective security checks whenever a specific risk or compliance requirement arises. SVA concentrates on the target issue, delivering fast results without the noise of a full scan.
Simple by default, flexible when needed
With BYOK, Dig Deeper and SVA offer Simple and Advanced AI provider configurations. You can also run investigations with Ostorlab-managed Cyber Models and credits.
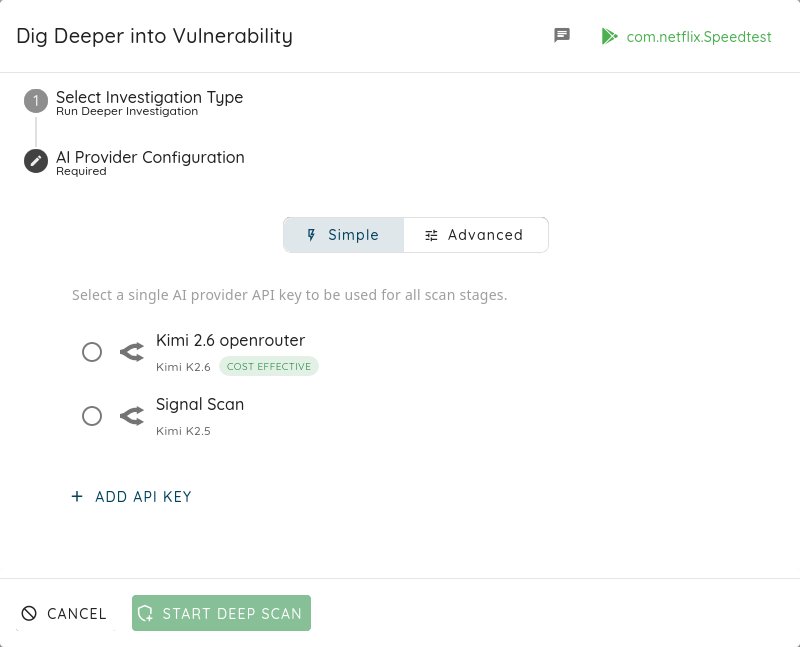
Simple Mode
Use one AI model for the full investigation workflow. Ideal for teams that want the easiest setup and a fast path to value.
Seamless Integrations with Your Tech Stack
Don't let security become a bottleneck. Ostorlab integrates directly with the tools your development and security teams already use, ensuring that vulnerability management is automated, traceable, and fast.
 Jira
 Linear
 Jenkins
 GitHub
 GitLab
 Bitbucket
 SAML
 Azure DevOps
 CircleCI
 GoCD
 TeamCity
 Okta
 Google Workspace
 OneLogin
 Azure Active Directory
 Slack
 Vanta
 ServiceNow
 Bitrise
 Harness
Trusted by Security Teams Worldwide
Discover why industry experts love working with our platform

Very efficient team, the support engineers are very good and knowledgeable. The product is always evolving and they take customer input very seriously.
A reliable product with unique features and a personalized approach to products.
The platform helped us evaluate our internal mobile applications easily and efficiently. The onboarding was smooth and the UI dynamic automation is great.
The product meets our needs perfectly and is easy to set up and use. The team is very reactive.
Very professional and technical. Five star. Excellent delivery.
We selected Ostorlab as our sole partner in providing mobile applications and web vulnerability scans. We have a very good partnership.
Their customer service is top notch and their product is constantly improving.
Easy to use and getting better with new updates, they are also quick to help and very efficient.
Great product, with amazing customer service, very useful, accurate, and straightforward to use.
Prompt support and personalized features highlighted.
I had a very excellent experience with Ostorlab as a MAST solution.
FAQ
Frequently asked questions
Straight answers on coverage, setup, and how results reach your team.
Can't find your answer? Book a demo or contact us.
Get Started with Dig Deeper
Investigate potential findings, test custom attack hypotheses and validate fixes with a focused AI assessment.